Web Application Pentesting: DAST, Black-Box Testing & Ethical Boundaries
Web application penetration testing plays a vital role in identifying security vulnerabilities, protecting sensitive data, and strengthening online security. Our agentic…
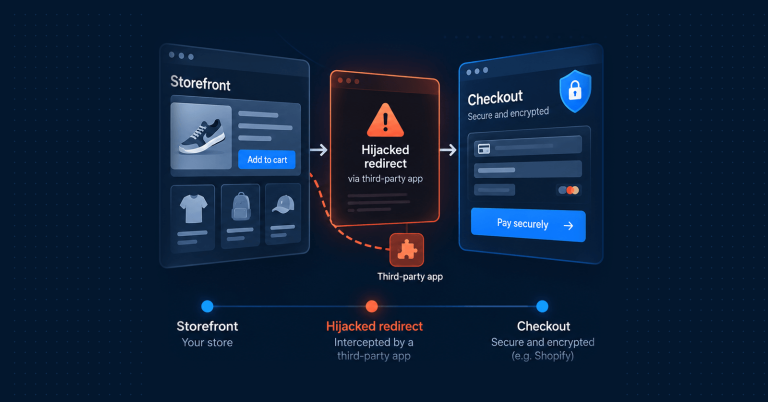
You can spend weeks preparing for Black Friday, then lose a sale when someone clicks “Pay now”. The checkout fails, they…
Recent Shopify checkout hijacking attacks reveal an important security risk that many online retailers may not realise exists: the difference between…
You may be familiar with web card skimming, where a fraudster replaces the payment iframe on an ecommerce site with a…
Yesterday (5 August), the WooCommerce team urged store owners to immediately update the WooCommerce Stripe Gateway following the discovery of a…
RapidSpike is proud to introduce CartShark, a cybersecurity platform that empowers ecommerce businesses to combat threats swiftly and effectively.
A sophisticated two-tier web skimming attack compromises electronics manufacturer Casio UK and at least 16 other ecommerce sites.
The latest notable attack discovered on 2nd September 2024, occurred on the Cisco merchandise website. We explore the intricacies of the…
RapidSpike, an industry leader in Synthetic User Journey website monitoring, is proud to announce that it has been awarded the highly…
We discuss why ecommerce managers need to focus on both website design and user experience to create highly performing websites.
Spring4Shell vulnerability – what you need to know from RapidSpike.
Log4j vulnerability – what you need to know from RapidSpike.