Web Application Pentesting: DAST, Black-Box Testing & Ethical Boundaries
Web application penetration testing plays a vital role in identifying security vulnerabilities, protecting sensitive data, and strengthening online security. Our agentic…
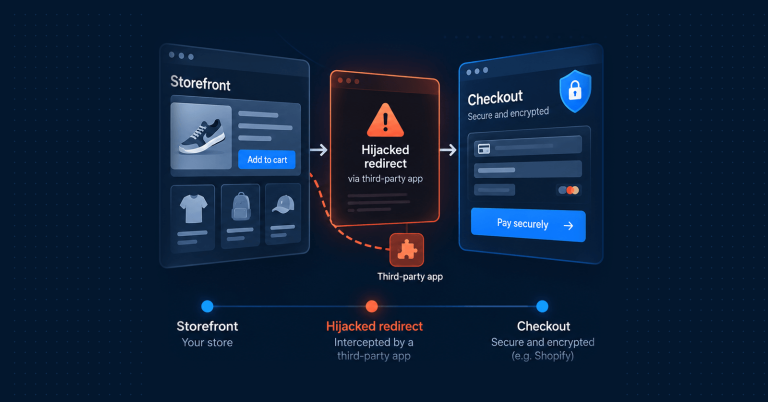
You can spend weeks preparing for Black Friday, then lose a sale when someone clicks âPay nowâ. The checkout fails, they…
Recent Shopify checkout hijacking attacks reveal an important security risk that many online retailers may not realise exists: the difference between…
You may be familiar with web card skimming, where a fraudster replaces the payment iframe on an ecommerce site with a…
Yesterday (5 August), the WooCommerce team urged store owners to immediately update the WooCommerce Stripe Gateway following the discovery of a…
Our 2026 roadmap is focused on one goal: turning monitoring data into trusted operational intelligence, take a look at whatâs to come.
Clear communication is everything when it comes to service availability. Whether youâre managing a critical website, a SaaS platform, or customer-facing…
Cyberattacks against ecommerce businesses are accelerating, and recent incidents show just how many different angles attackers are exploiting. Whether itâs phishing…
RapidSpike is proud to introduce CartShark, a cybersecurity platform that empowers ecommerce businesses to combat threats swiftly and effectively.
RapidSpike’s ilert integration helps transform alerts into actionable incidents, ensuring the right teams are notified effectively.
A sophisticated two-tier web skimming attack compromises electronics manufacturer Casio UK and at least 16 other ecommerce sites.
In December 2024, it was reported that the European Space Agency’s (ESA) official online store suffered a Magecart attack aimed at compromising customersâ…